Unit 42
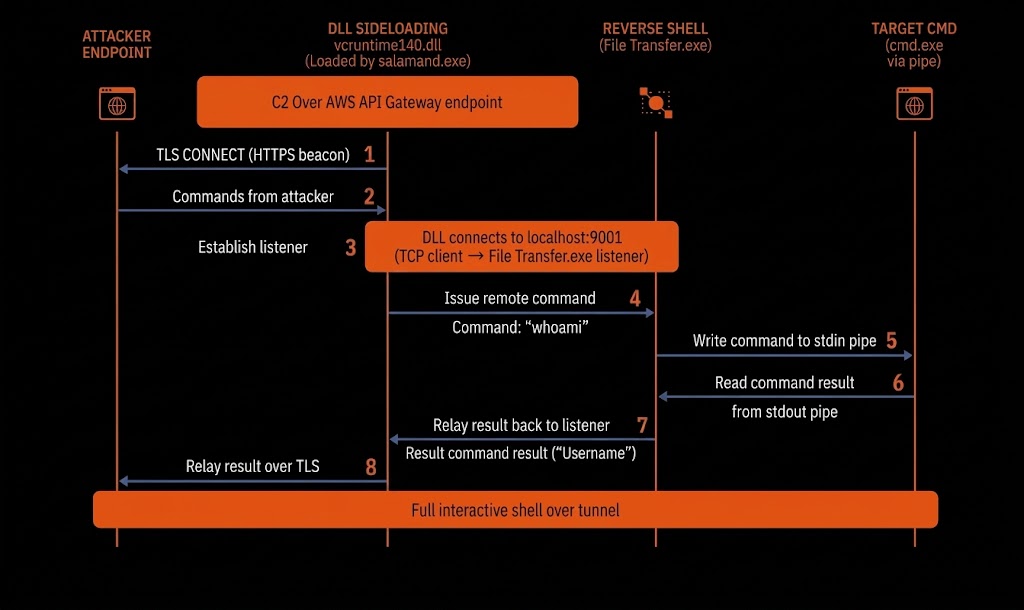
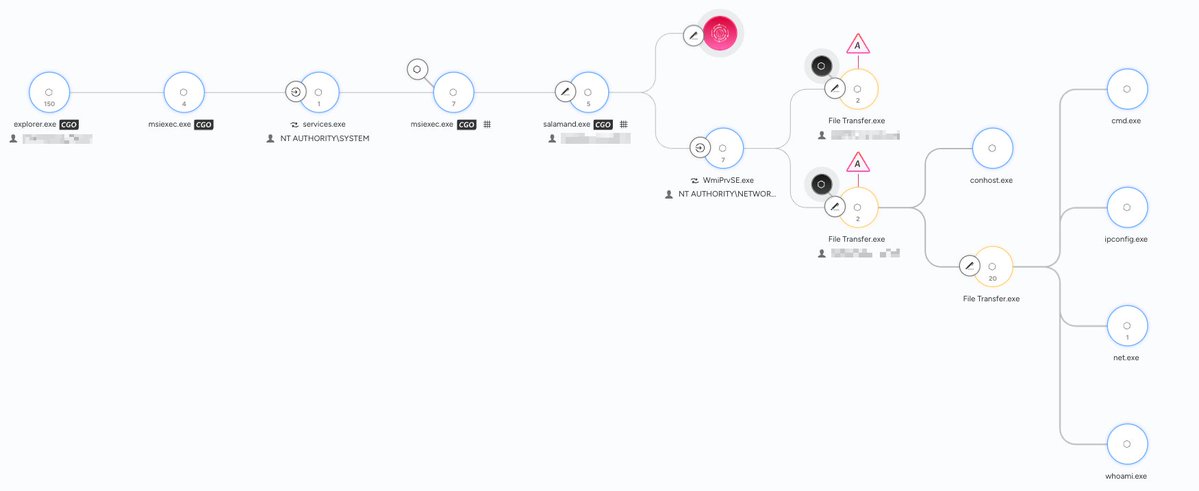
Fake IT support campaign delivers a malicious MSI that sideloads a trojanized DLL via a signed binary, then uses WMI to launch a custom reverse shell tunneled over a local port (localhost:9001) to an AWS API Gateway C2. Detection and indicators: https://bit.ly/4ycFn7h