V12
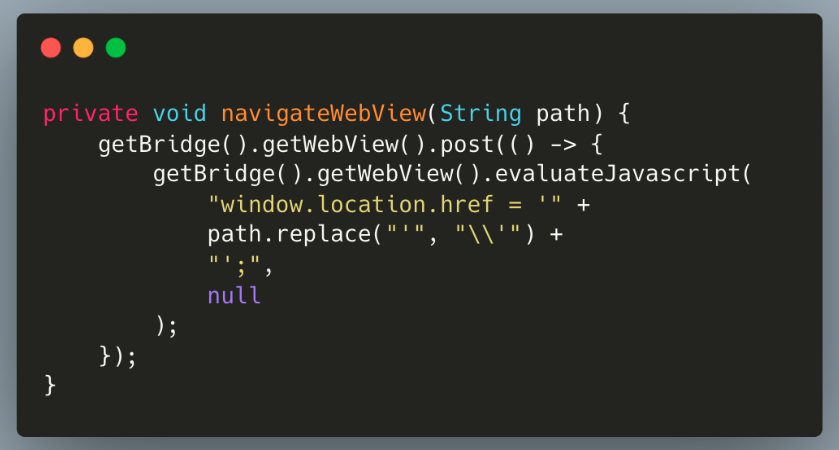
Ditto tries to sanitize <PATH> by escaping `'` before passing into JavaScript. But it does not escape backslashes. A path containing `\'` becomes `\\'`: an escaped backslash followed by a live quote. The string ends. Attacker-controlled JavaScript begins.